Data Residency and Sovereignty with Object Storage
Residency and sovereignty are not the same—and that distinction can save you in court.
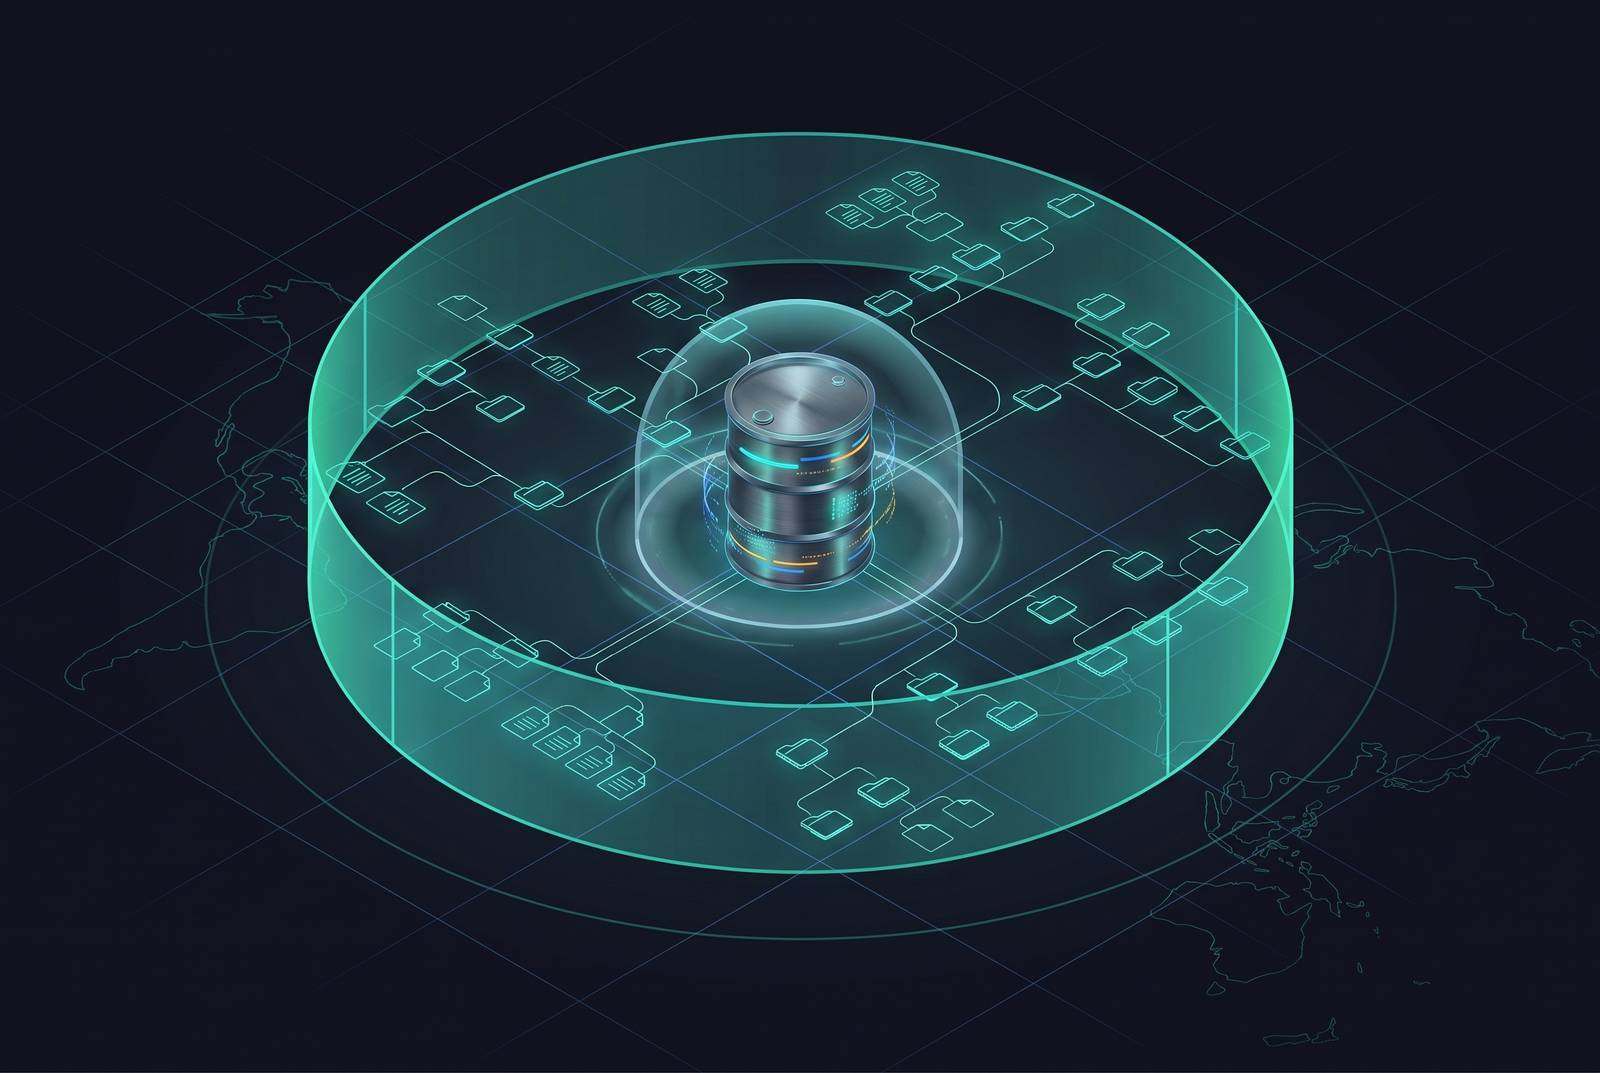
Data residency tells you which country your data physically sits in. Data sovereignty tells you who actually controls it, and those are two very different questions with two very different answers. Get the distinction wrong, and you can build a storage setup that sails through an audit and still gets torn apart the first time a foreign court asserts jurisdiction over it.
Residency puts your data behind a door in the right country. Sovereignty is about who else holds a key to that door, and whether a judge somewhere can force them to use it. TierPoint has made this point: residency is one piece of sovereignty, not a stand-in for the whole thing. A data center can sit in Frankfurt and still answer to a courtroom in the vendor's home country, if the company running it is headquartered there. Choosing an object storage strategy across borders means solving for the key, not just the door. Most companies still buy the door and call it done.
How the regulatory landscape made this gap impossible to ignore
Countries with data protection laws on the books have climbed from 76 to more than 120, and the count keeps rising, jurisdiction by jurisdiction, with no sign of leveling off.
The EU has built out the most rules in the shortest time. The EU Data Act took effect January 11, 2024, and started applying September 12, 2025. Chapter VII tells cloud providers, and their customers, to block unlawful access from non-EU governments to non-personal data, and to refuse or flag any access request that conflicts with EU law. NIS-2 raised the security bar for critical infrastructure, adopted in 2022, due for transposition by October 2024. DORA landed for EU financial services on January 17, 2025. The EU AI Act's majority of rules kick in August 2, 2026, though the toughest obligations for high-risk systems got pushed further out, to December 2027 and August 2028, under the Digital Omnibus on AI. Even delayed, data governance for AI has become a technical requirement now, not a nice-to-have.
Outside the EU, India's data protection framework is evolving with new compliance expectations, and the UK is drifting from EU GDPR post-Brexit, its adequacy status under review through December 2025. Layer in more than 120 countries running their own, often contradictory, localization rules, and the map stops being a map. It's more like a patchwork quilt sewn by a hundred different tailors who never spoke to each other.
That patchwork is exactly why teams keep landing on object storage as the layer where sovereignty actually gets enforced, which is where the next problem starts.
The CLOUD Act conflict that residency alone cannot solve
A cross-border disclosure law lets one country's authorities compel cloud providers headquartered there to hand over data, no matter where that data physically sits. One data center location or another, it doesn't matter. If the company answers to that country's law, so does the data, wherever the servers happen to be humming.
2025 gave the industry its clearest proof point yet. Microsoft told the French Senate it could not guarantee data sovereignty for EU customers. That's not a hedge or a caveat buried in fine print. That's the provider saying, on record, that residency promises from U.S.-owned companies have a structural ceiling built into them.
Move into 2026, and the conflict stops being theoretical. A disclosure order compelling delivery of EU resident data to a foreign government collides head-on with GDPR provisions that forbid exactly that disclosure without EU legal sign-off. Two legal systems, both mandatory, pointing in opposite directions, and the storage provider caught in the middle doesn't get to pick a side.
The UK adds its own wrinkle. The UK-US Data Access Agreement, active since October 2022, makes data requests faster and easier to fulfill, which raises the stakes for UK organizations still working through post-Brexit compliance questions of their own.
Residency puts data on European soil. Sovereignty requires that nobody with access to that data answers to a foreign government's compelled-disclosure powers, and those are separate architectural properties. By 2026, the industry has largely stopped asking "where does the data sit" and started asking "who controls the stack." That second question is the one storage architecture now has to answer, and residency alone was never built to answer it.
Why object storage became the practical layer for sovereignty compliance
Object storage fits this problem because of how it's built: flat structure, spread across regions, with metadata rich enough to enforce jurisdiction-level rules at scale. That's useful for AI training data. It's also useful for a compliance officer who needs to prove, in writing, where every byte lives, not just gesture at a diagram.
S3 API compatibility matters more than it sounds like it should. Full compatibility means an organization can move applications and backup tools without rewriting code, protecting a technology investment nobody wants to rebuild just to satisfy a residency rule. Rip out a backup pipeline and replace it because a regulator changed the rules, and you've turned a policy update into a six-month engineering project.
Country-level geofencing is the concrete technical answer to "prove it stays here." Done right, it guarantees storage happens exclusively in a defined region. Immutability, through S3 Object Lock and WORM (write once, read many) configurations, does double duty: it makes backups tamper-proof and satisfies retention rules baked into GDPR and related compliance frameworks at the same time, no extra tooling required.
Knowing these technical controls exist is one thing. Picking a provider that actually delivers them, instead of listing them on a feature page, is the harder problem, and it's the one most teams get wrong.
What "sovereign-by-design" means in storage architecture and where providers differ
Sovereignty is a guarantee only the architecture itself can enforce. It's a structural fact about whether a provider is even capable of breaking the promise, not a policy they've chosen to keep. A sovereign-by-design setup means the provider never held the kind of access that would let them betray it in the first place, even under legal pressure from their own government.
Where a provider is headquartered matters as much as where its data centers sit, and this is the part most buyers skip past. A company owned and governed entirely under EU law removes CLOUD Act exposure structurally, by definition. A company headquartered outside the EU but running EU data centers does not, no matter what the contract says. Read the sovereignty clause twice if a vendor's headquarters and their marketing copy don't match up.
A few architectural controls separate real sovereignty from marketing copy:
- Country-level geofencing enforced at the storage layer itself, not just written into a policy document somewhere
- Immutable storage with Object Lock in compliance mode, for audit trails that actually hold up in court
- Granular identity and access management, with multi-factor authentication and support for external identity providers
- Zero-egress or predictable-egress pricing, since unpredictable restore fees push teams toward moving data around in ways that quietly break residency guarantees
- Always-hot architecture, since tiering delays blur exactly where data sits at any given moment, a detail that's easy to miss until an auditor asks about it directly
There's also the vendor-access question, and it's the one that separates real sovereignty from a promise. A provider that never keeps a persistent copy of customer data outside the customer's own account, and whose access can be revoked without losing data or triggering a migration, satisfies sovereignty as an architectural fact. Not a policy. A fact. The customer's bucket stays the actual source of truth, full stop.
Storage-agnostic mounting across S3, GCS, R2, and Azure Blob, without ETL jobs or data migration, lets an organization keep control over which jurisdiction's infrastructure gets used, and switch later without rebuilding a pipeline from scratch. The AI Act's August 2026 enforcement date turns data governance into a compliance dependency, not a bonus feature buried in a vendor's pitch deck.
The multi-jurisdiction complexity that no single-region strategy fully resolves
Serve customers in the EU, China, India, and Russia at once, and there's a decent chance you need separate storage setups with different transfer mechanisms for each one. What passes muster in Brussels can get you in trouble in Beijing, and no single region-locked architecture papers over that gap.
Picture an EU citizen logging into a company account from Singapore on a business trip. That one login raises real GDPR questions that geofencing by itself doesn't answer, because geolocation isn't reliable enough to lean on fully to begin with. IP-based location detection is shaky in mobile scenarios, and VPNs or proxies chip away at whatever accuracy is left. Technical controls at the user-access layer are imperfect. Full stop, no asterisk.
Analytics and machine learning pipelines add another layer of mess. Training data pulled together from multiple regions creates jurisdictional ambiguity that storage-layer controls alone can't fix, since governance has to extend into how the data gets processed, not just where it's parked on disk.
Multi-cloud and hybrid setups are a partial answer, spreading data across providers and regions to match local rules. Cloudian HyperStore is one example: cloud-agnostic S3 storage that deploys on-premises and across AWS, Google, and Azure under a single management layer. But connecting providers together is genuinely hard, not a checkbox exercise, and multi-cloud strategies frequently fall short of expectations in practice. Multi-cloud sovereignty comes with its own execution risk bolted on.
Architecture can shrink legal exposure. It cannot replace a lawyer reviewing each jurisdiction, one at a time, and anyone selling you otherwise is selling you a shortcut that doesn't exist.
How AI training workloads are raising the sovereignty stakes for storage teams
Storage bottlenecks are already limiting how well AI systems perform and scale for a large share of organizations running them, and a good chunk of that data isn't even AI-ready to begin with. Feed a training pipeline data that hasn't been cleaned, tagged, or governed properly, and sovereignty becomes the least of the problems on the list.
The AI Act's August 2026 enforcement date turns "where is the training data governed" into a technical compliance question, not just a legal one sitting in outside counsel's inbox. Train a model on data sitting outside its permitted jurisdiction, and the exposure stops being theoretical. It becomes a regulatory problem with a fine attached.
Sovereign storage still has to perform, though, because a GPU cluster sitting idle waiting on data is an expensive way to prove a point about compliance. Data loading used to eat up over a third of total training time in setups bottlenecked at the processor; better architecture brought that down to a fraction of that. The assumption that sovereign storage has to mean slow storage doesn't hold up under that math. Geofencing and throughput can be designed in together, from the start, rather than traded off against each other like a zero-sum negotiation.
Storage-agnostic mounting matters here too. When a filesystem layer sits on top of whatever jurisdiction-appropriate object store is in use, without ETL jobs or copying data around, teams stop building data-movement pipelines and just start training models. The sovereignty rule becomes a routing decision instead of a re-architecture project that eats a quarter.
AI workloads that need the same source data across repeated runs need storage that's sovereignty-compliant, fast, and stable across sessions, all three at once, every single time. Scratch storage that resets between sessions doesn't cut it, and pretending otherwise just moves the failure further downstream.
What to evaluate when choosing an object storage approach for sovereignty compliance
Start with the provider's legal home, not the data center's street address. Legal domicile is what determines CLOUD Act exposure, and it's the single question most procurement checklists skip. A provider that's EU-owned and EU-governed closes off a risk that residency-only claims leave wide open, no matter how many data centers they list on the sales page.
Then check that the technical controls are actually enforced, not just promised in a slide deck:
- Geofencing enforced at the storage layer itself, not buried in a policy PDF nobody reads
- Object Lock or WORM available in compliance mode, built for GDPR and regulatory audit trails
- IAM that's genuinely granular: role-based, MFA-enforced, compatible with external identity providers
Ask the vendor-access question directly, and don't accept a vague answer. Does the provider keep a copy of customer data outside the customer's own account? Can access be pulled without losing data or forcing a migration? A provider that literally cannot access the data cannot be forced to hand it over, no matter what agency comes knocking on their door.
Check how deep the S3 compatibility actually goes: versioning, lifecycle management, object tagging, compatibility with the backup tools already in use, not just basic GET and PUT calls. Shallow compatibility forces a re-architecture down the line, and that re-architecture is exactly where sovereignty gaps sneak back in through the side door.
Look at portability too. The ability to mount across S3, GCS, R2, and Azure Blob without a migration project means a jurisdiction change becomes a routing decision, not a six-month engineering effort with its own budget line. The EU Data Act's rules on data portability and provider switching, enforceable from September 12, 2025, with a full ban on switching fees arriving in January 2027, make this a regulatory expectation now, not a nice-to-have.
Cost predictability counts as a sovereignty control in its own right. Surprise egress fees create pressure to move data around in ways that quietly break residency guarantees, the exact opposite of what the architecture was supposed to protect. Zero-egress or flat-egress pricing removes that temptation before it ever shows up.
For AI training specifically, check throughput and latency inside the sovereign region itself. Geofencing that locks data to one region is only as good as the storage serving GPU workloads from that same region, fast enough that the region requirement doesn't turn into a performance tax nobody budgeted for.
Sovereignty has to be designed in before the breach happens or the regulator calls, not bolted on after the fact like a fire escape added to a building that's already on fire. Organizations that treat data geography as a genuine architecture decision, and not a box to check on a compliance form, are the ones that get to operate across borders without an existential legal problem waiting quietly on the other side.
Sources
- Understanding Data Sovereignty in the Cloud
- The Global Data Residency Crisis: How Enterprises Can Navigate Geolocation, Storage, and Privacy Compliance Without Sacrificing Performance - Security Boulevard
- The Great Cloud Charade: Why "Data Residency" Isn't "Data Sovereignty"
- kiteworks.com
- CLOUD Act - What It Means for EU Data Sovereignty
- kiteworks.com
- rtinsights.com
- cloudian.com